Every security leader we talk to is working on two problems at once:
These are not separate problems. The same agent capabilities that make AI attacks dangerous also make enterprise agents powerful. Solving one issue without the other leaves a gap.
To meet both challenges, organizations need to move toward an architecture of Autonomous Security. Offensive AI agents continuously probe the environment the way a real adversary would. What they find trains and tunes defensive AI, so defenses improve at the same speed attacks do.
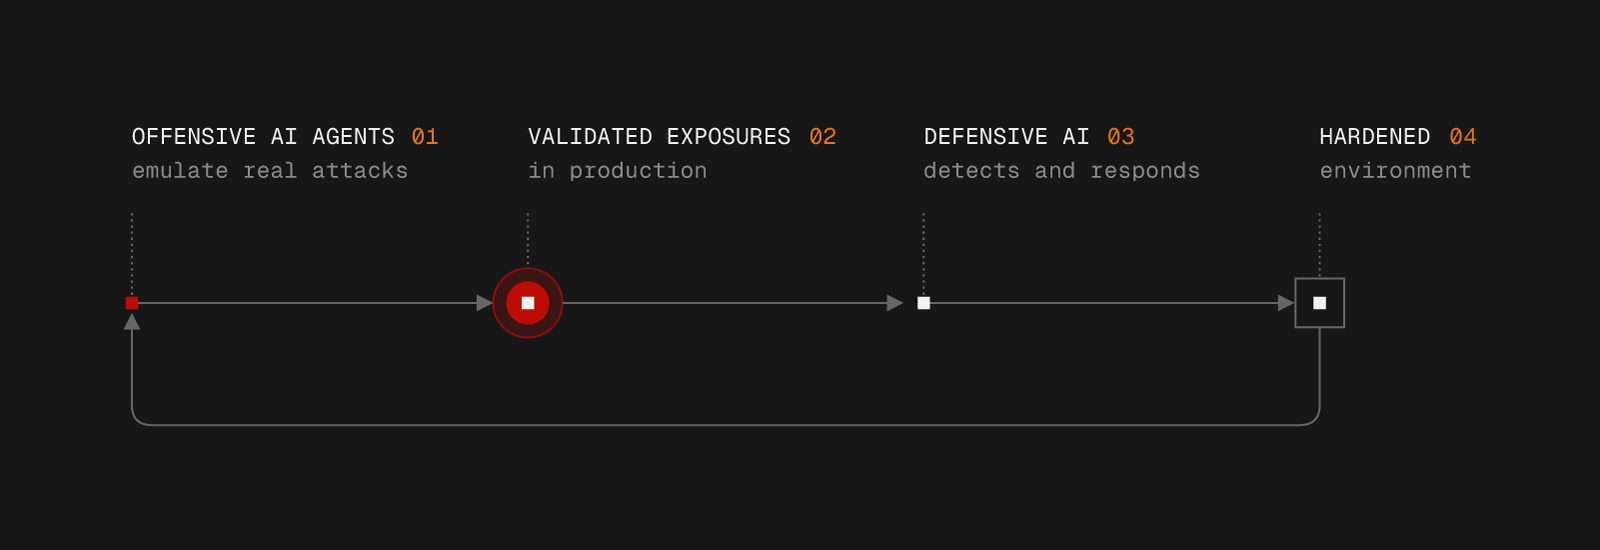
Every organization needs to understand its exposure to AI attacks in its production environment, safely. Staging environments and point-in-time assessments miss how an autonomous adversary would actually move through live systems.
Running offensive agents against production environments raises the same question every enterprise now asks about its own agents: how do you let an autonomous system act with real capability while guaranteeing it stays inside the lines?
Asking a model to behave is not a control. Safety has to be enforced by systems outside the model and the agent harness.
Armadin takes a multilayer approach:
No single layer is trusted on its own. Each one assumes the layer above it can fail.
We're excited to be among the organizations working with NVIDIA to deploy NVIDIA Open Agent Safety Platform technologies. NVIDIA OpenShell open source software provides a secure runtime boundary that governs agent actions. NVIDIA Sentry reference system design uses NVIDIA DOCA on NVIDIA BlueField-4 DPUs for hardware-isolated, out-of-band monitoring and policy enforcement. The platform is built similar to the way autonomous vehicles are built: layered controls with redundancy at every level, and a shared-responsibility model across software, hardware, and compute. That is the same architecture Armadin already uses to keep offensive agents safe.
This means the safety guarantees behind Armadin's AI attacks can extend from our software layer down to the infrastructure, with controls an agent cannot see or bypass.
Armadin is contributing to NVIDIA OpenShell, the open source runtime at the center of the platform. Offensive agents are a demanding test of any runtime boundary: they are designed to find and use every opening. What we learn keeping our own agents contained is exactly what makes a boundary stronger for everyone else's.
Autonomous Security only works if autonomy is safe. Armadin will keep building offensive AI that runs against production with enforceable limits, and we'll keep contributing what we learn to the open tools the industry depends on.